Access reviews and incidents
Auditors ask two things that are hard to answer from memory: "is everyone's access still needed?" and "what went wrong with your AI systems, and who did you tell?". Vidai keeps both as records: an access review checks every role and key and keeps or revokes each, and the serious-incident register records what happened, to which systems, and who it was reported to. Both go into the evidence pack.
Access reviews
Proof › Access reviews lists every role held and every key that isn't revoked, as they are when the review starts. For each item you see whose access it is, what it is, and when a key was last used. Tick what you've checked, then Keep or Revoke: a revoked role is removed and a revoked key stops working at once. A note can go with each decision, for the auditor.
- Nobody decides on their own access. Your own items say Yours: another reviewer decides; another organisation admin or a Compliance officer decides them.
- The last organisation admin's role is never removed.
- One review is open at a time. When every item is decided, Close the review…; once closed, nothing changes, and its Result says what was kept and revoked, how many people with roles use multi-factor sign-in, and who reviewed.
The evidence pack carries the result of the last closed review.
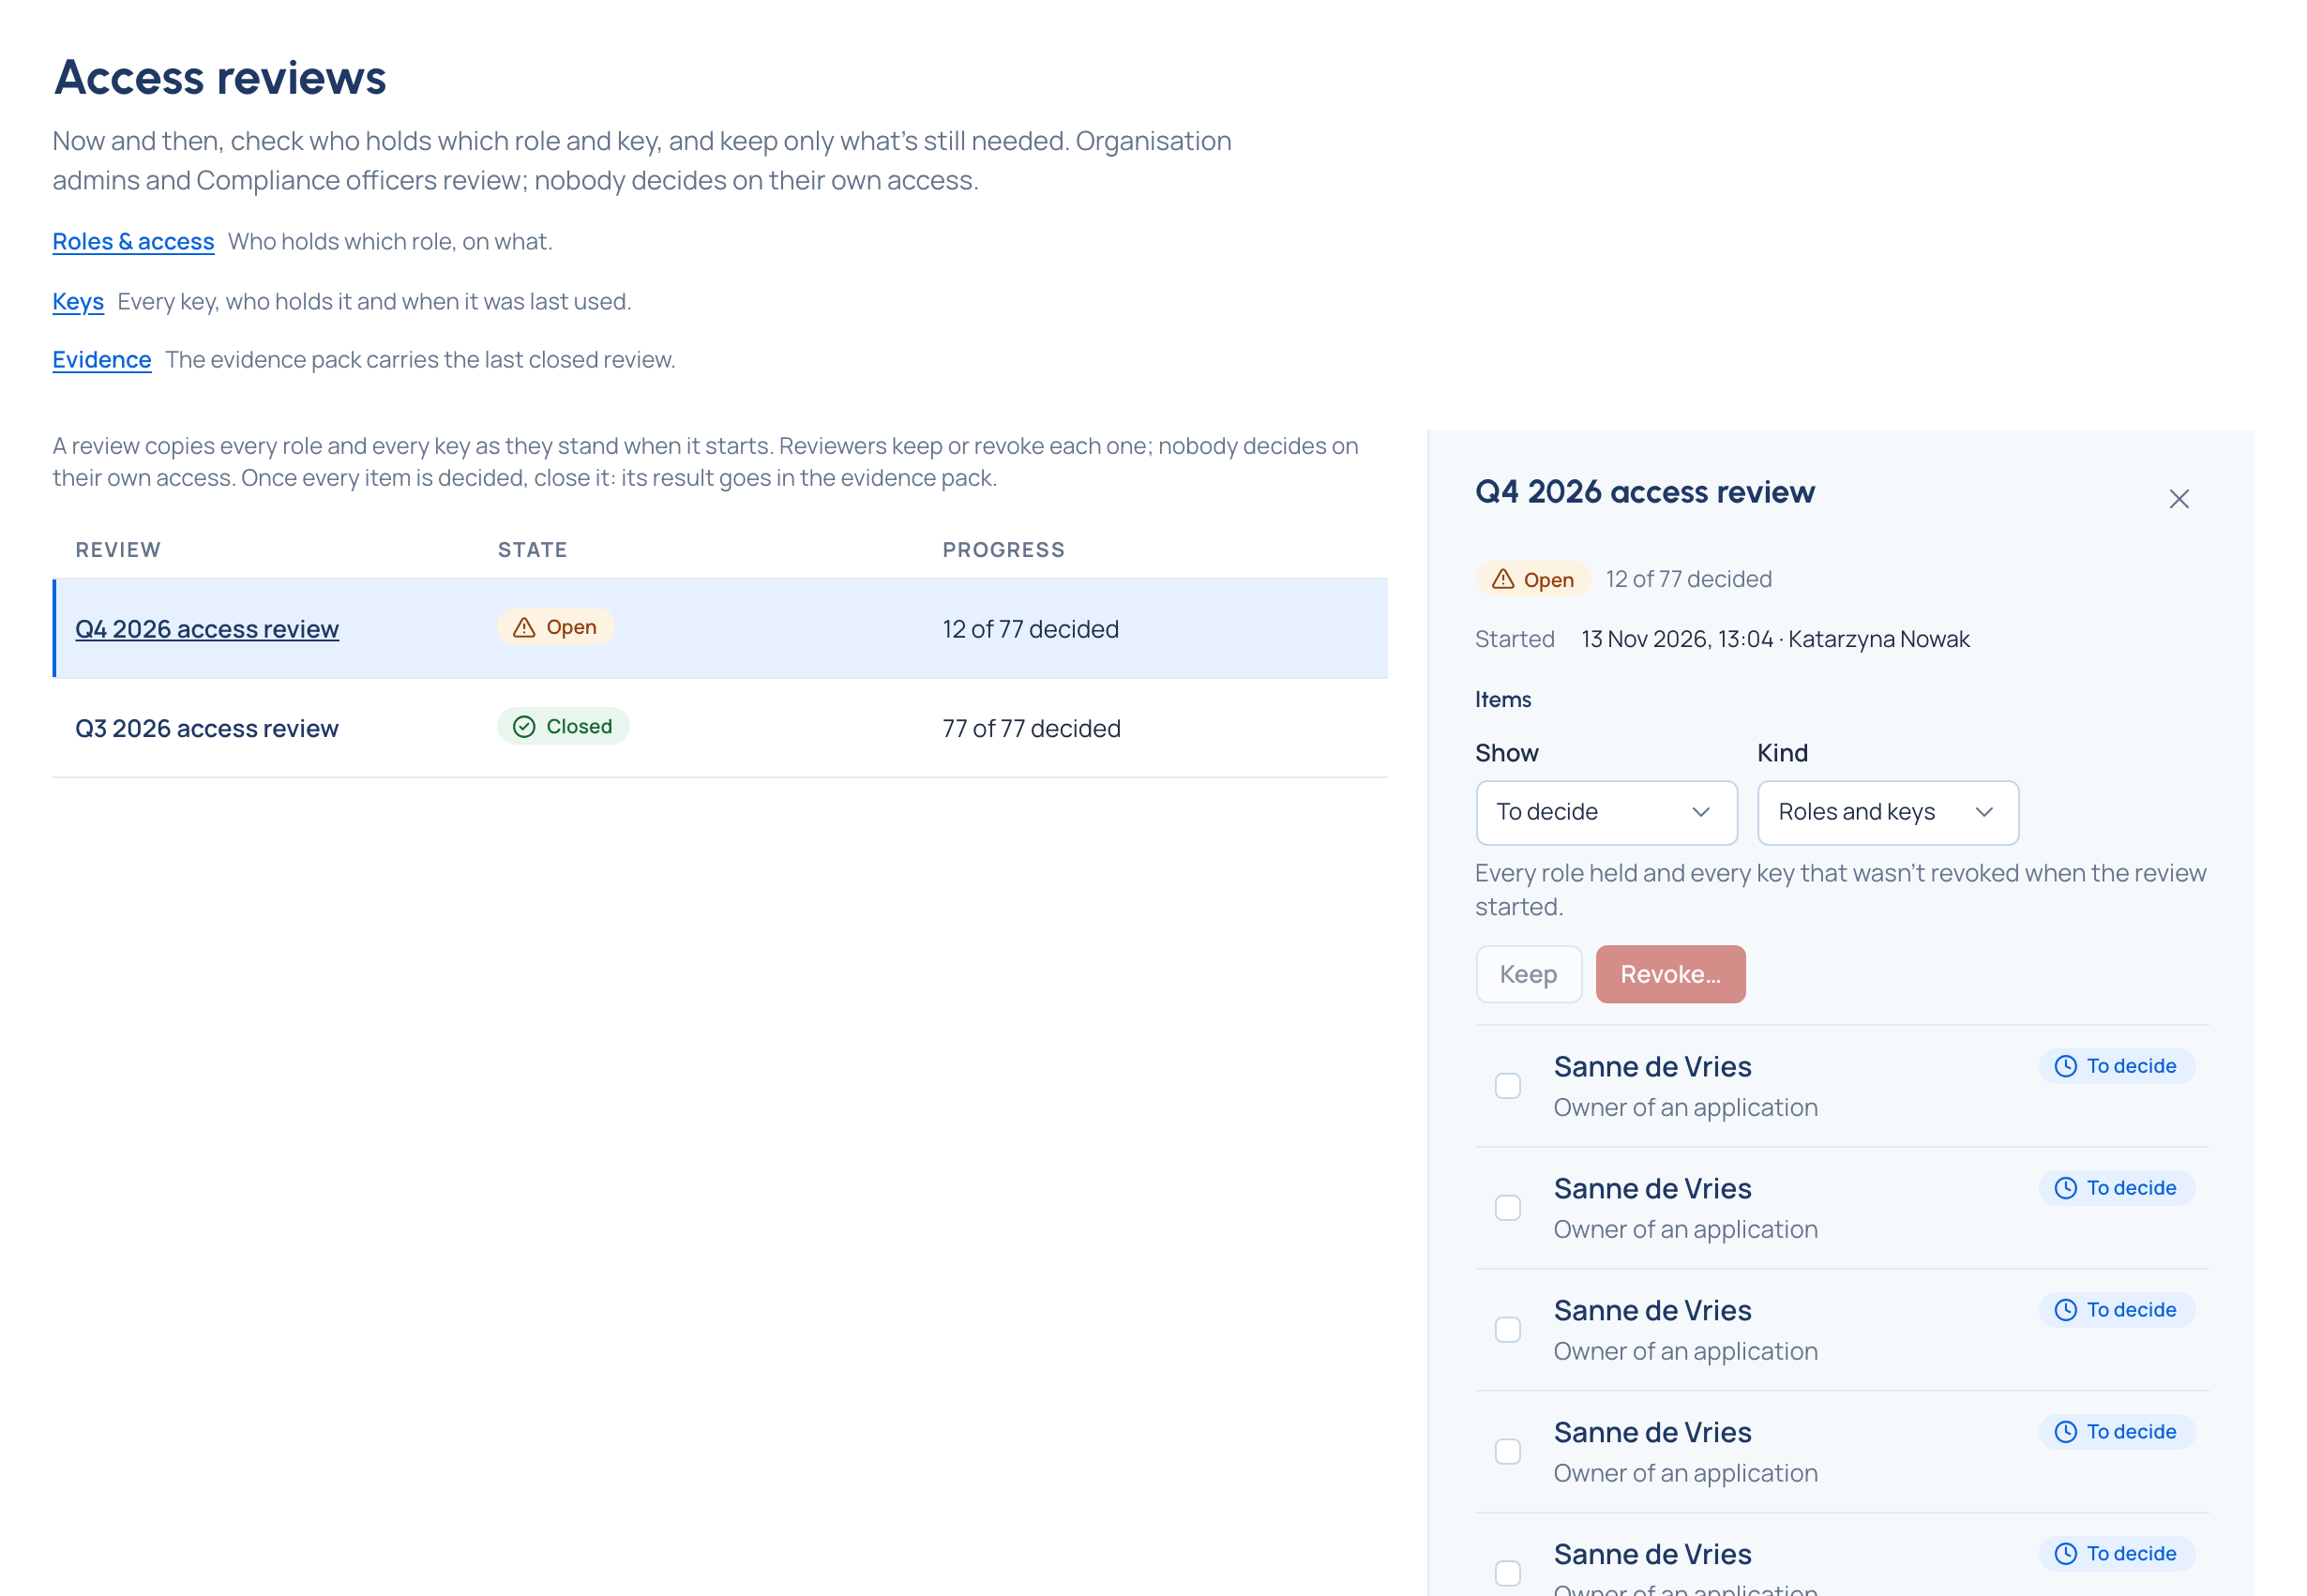
Organisation admins and Compliance officers run reviews; it's in every edition.
Serious incidents Enterprise
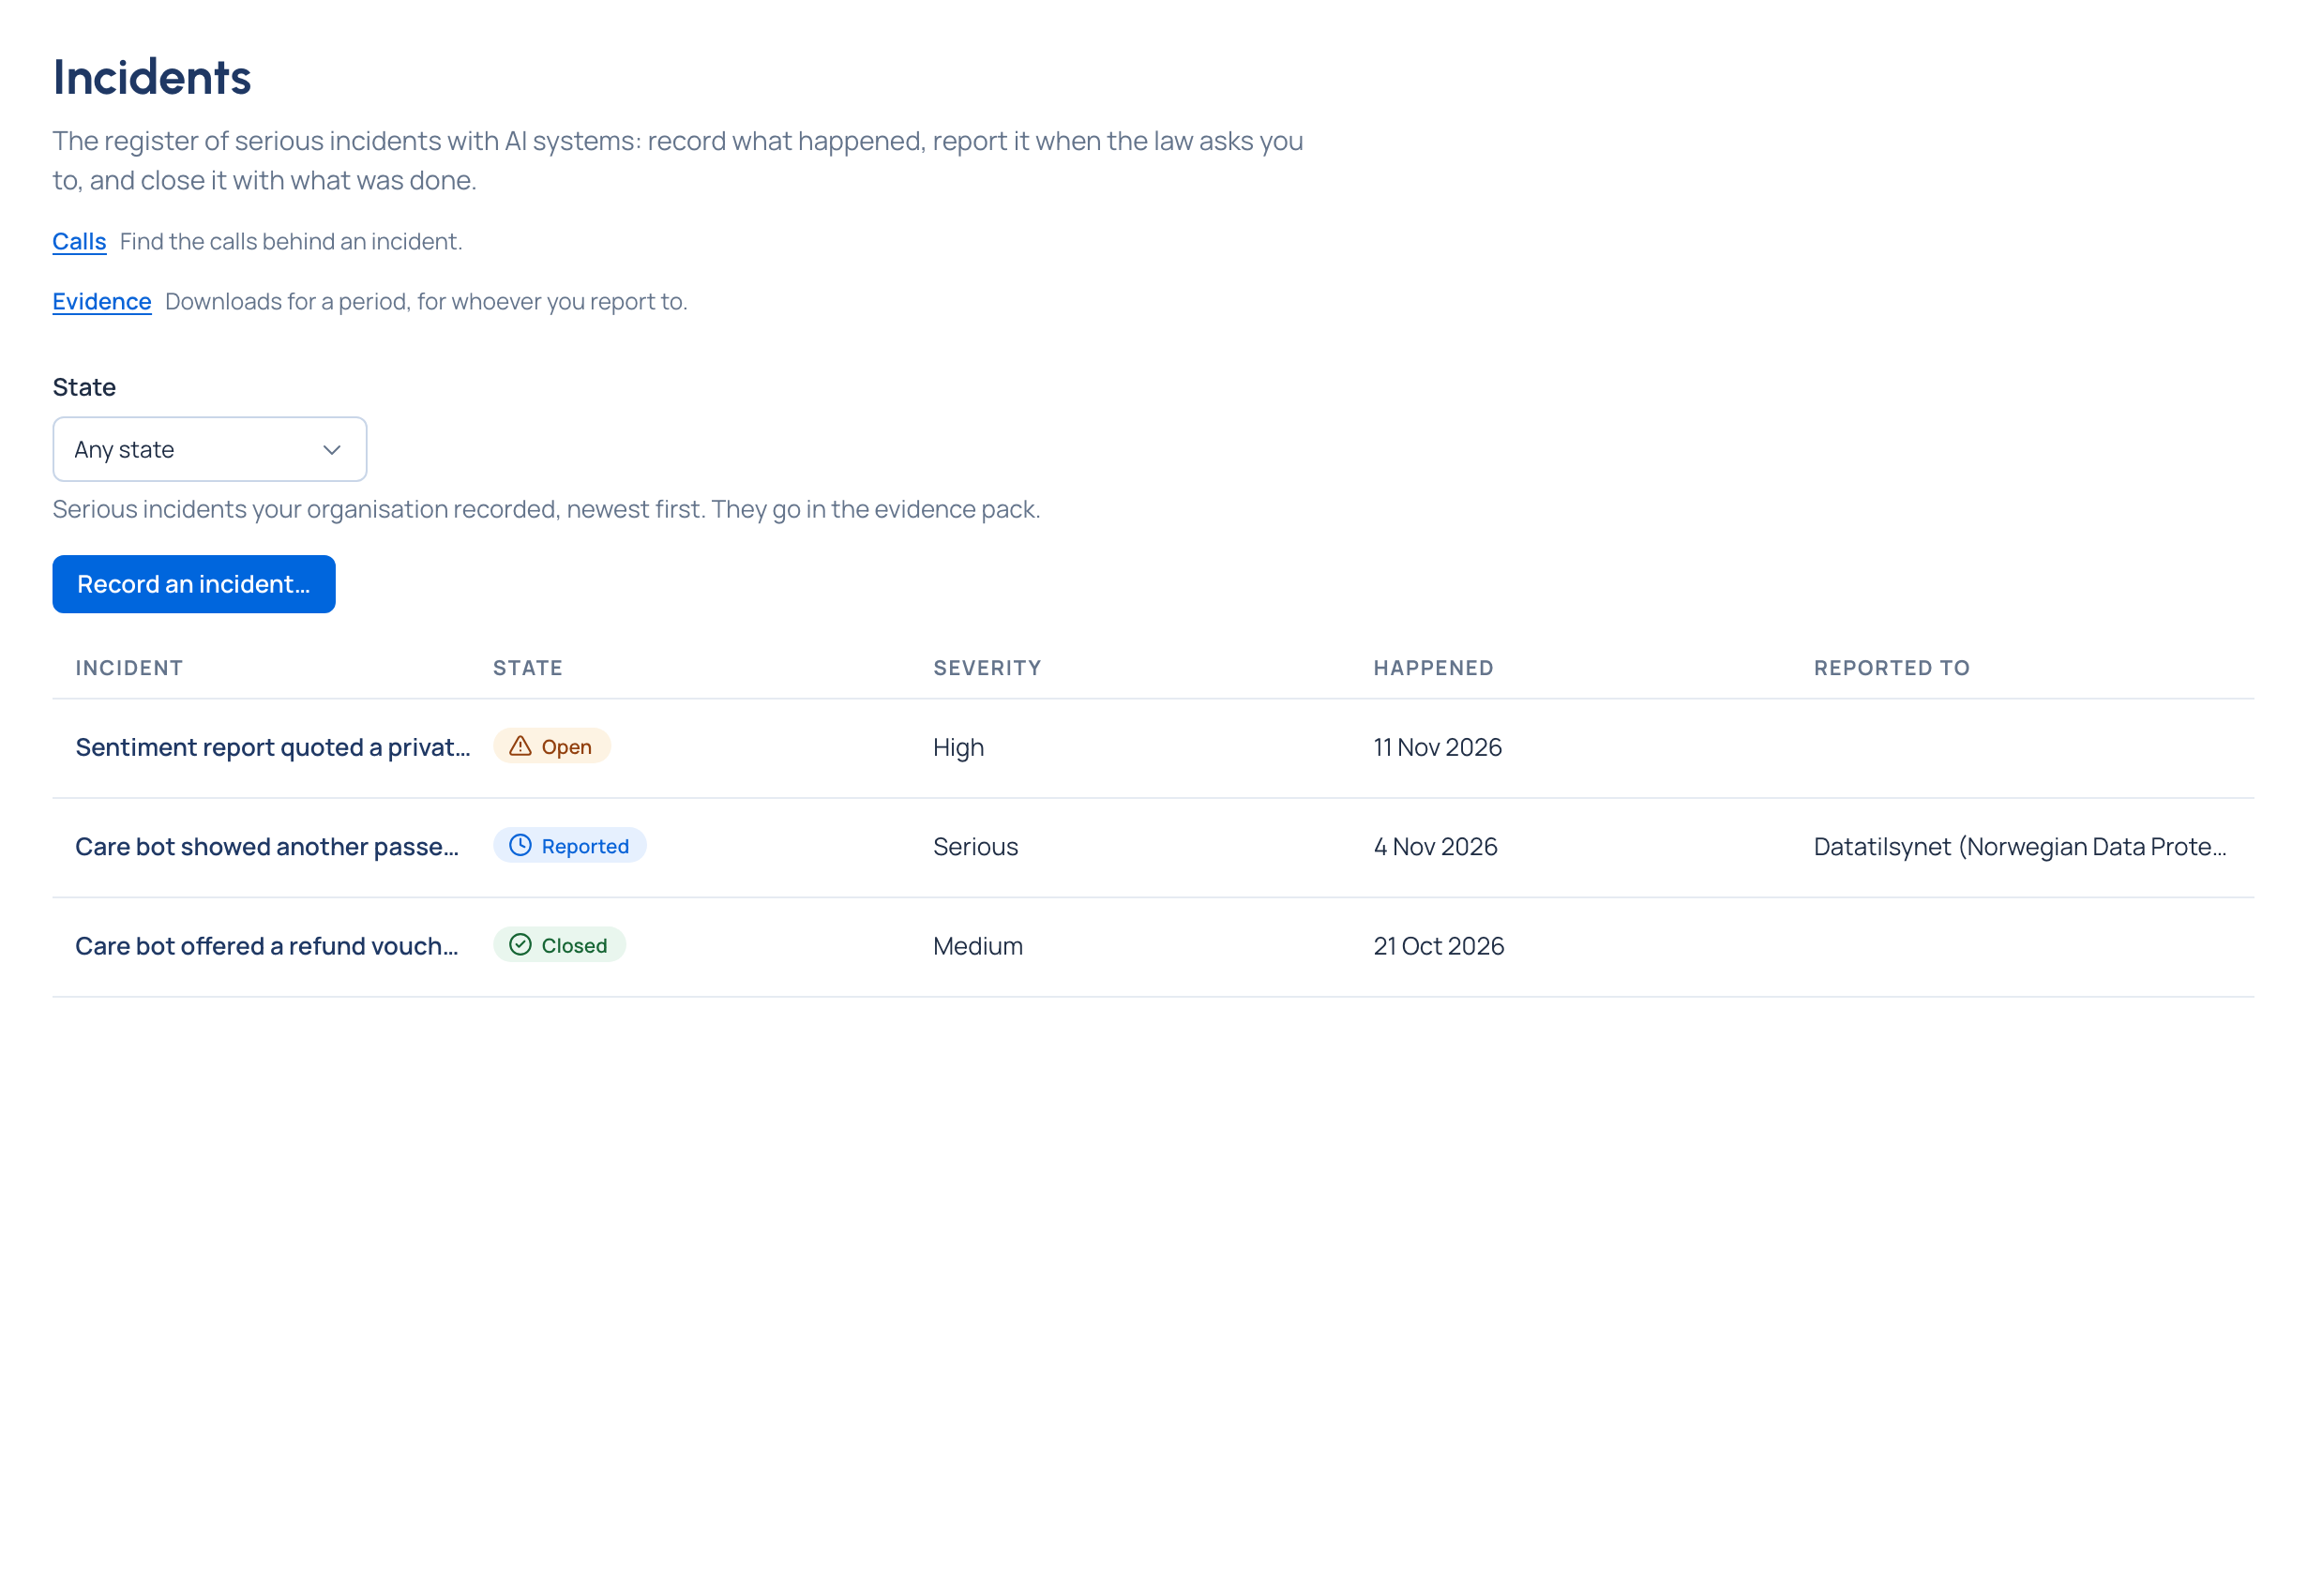
Proof › Incidents is your organisation's register of serious incidents involving AI systems: a title, the severity (low, medium, high, serious), when it happened and when it was found, what happened, and the applications, agents or teams involved.
flowchart LR
  Rec[Record an incident] --> Open[Open]
  Open -->|Mark as reported…<br/>to whom, when| Rep[Reported]
  Rep -->|Close…| Closed[Closed, still in<br/>the register and evidence]
Vidai doesn't send the report: it records who you made it to (a market surveillance authority, say) and when. A correction to the dates is kept in the audit log with before and after. Compliance officers and organisation admins record and change incidents; organisation viewers read the register.
What Enterprise includes depends on the features your licence includes. On Community, the register isn't installed.
Related
- People and roles · Keys: what a review checks
- Risk and AI systems: the systems an incident names
- Tamper evidence: the evidence pack that carries both
- Safety switches: stopping traffic during an incident