Named compliance policies
The problem. "GDPR for the booking assistant" is one intent, but in most stacks it's a dozen settings in several tools, each changed separately, with nothing tying them together. With Vidai, a compliance policy gathers the rules that serve one purpose under one name, with a regulation, an owner, a review date and a state. You move it from watching to enforcing in one step, and every call it acted on names it.
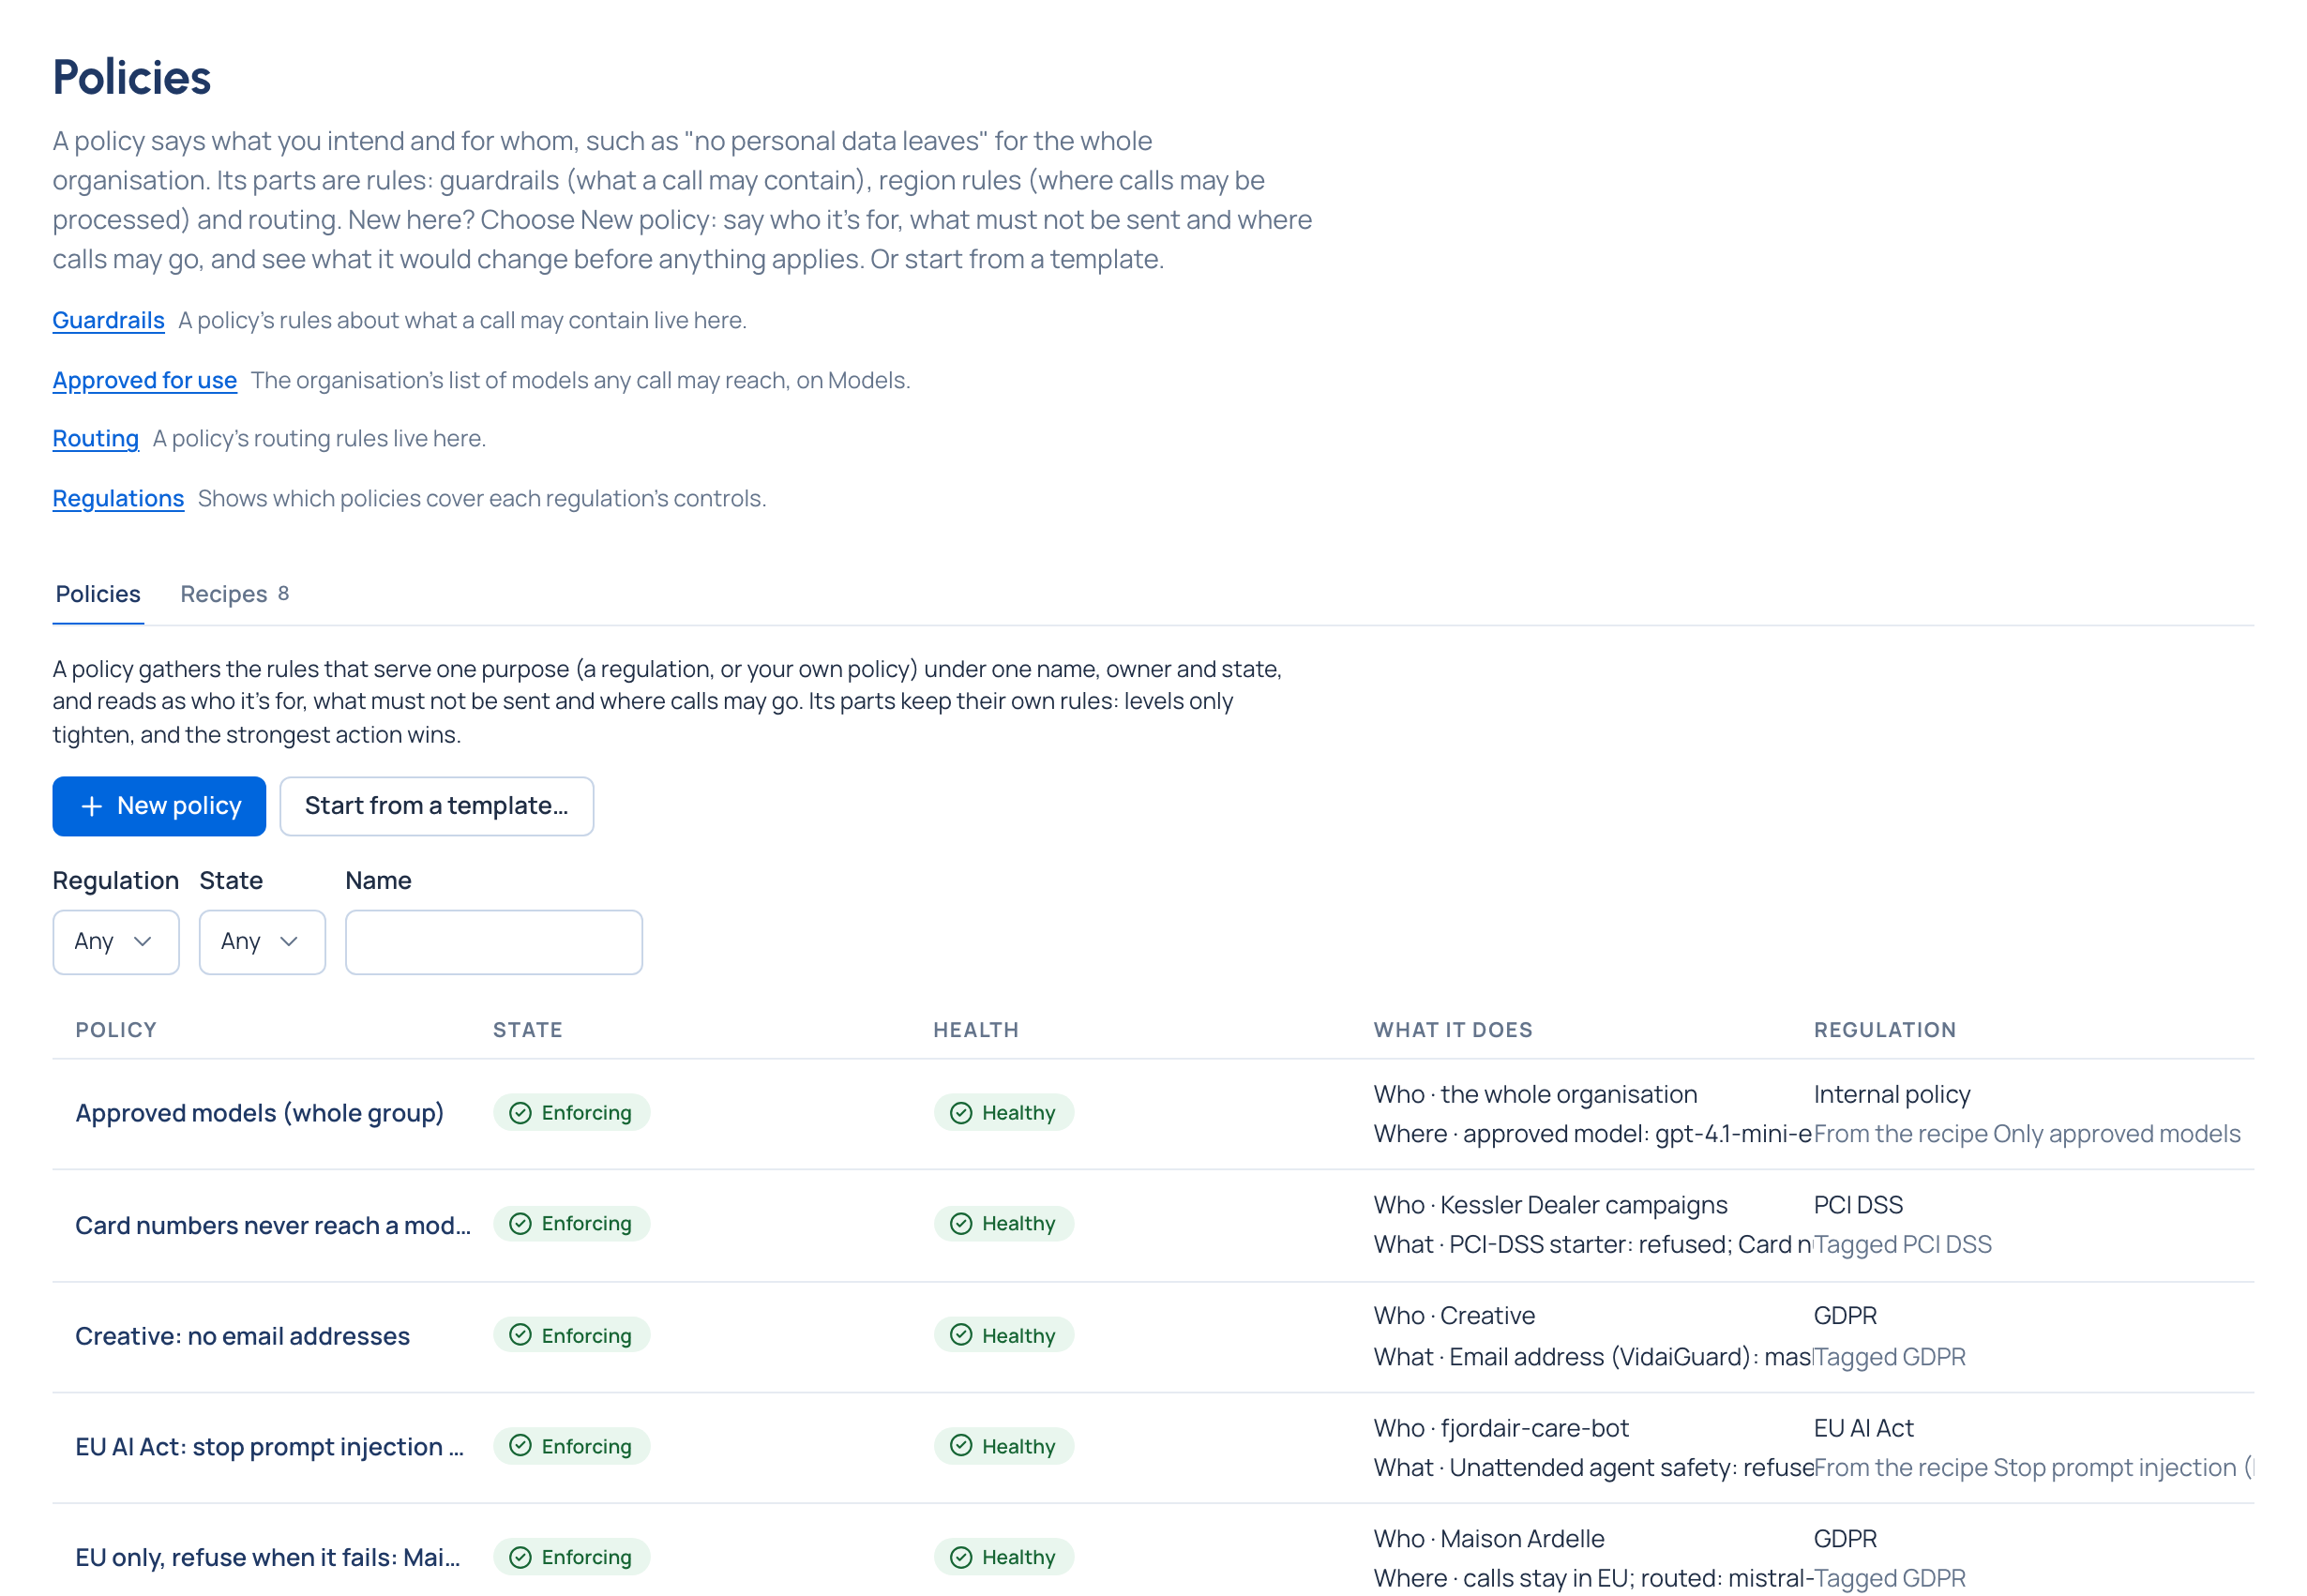
What a policy holds
A policy's parts are ordinary rules: guardrails, region rules and compliance routes, approved models, routing rules and budgets. Each part keeps its own behaviour: levels only tighten, and the strongest action wins. The policy names and governs them; it never decides a call on its own.
Each row reads back as sentences: Who it's for, What its guardrails find and do ("Email address: masked"), Where calls may go ("calls stay in EU"), How much (a budget it holds).
Three ways to make one
- From a recipe: answer a few questions and the recipe makes the policy and its parts in one change. Built-in recipes: Keep an application in a region, Personal data stays out, Protect health data, Keep card numbers out, No secrets in prompts, Stop prompt injection, Only approved models, Spend limit. One policy can hold several recipes. See Apply a recipe.
- From a regulation you follow: its recommended policies are offered when you follow it, and made watching first. See Follow a regulation.
- By hand: New policy asks who it's for, what must not be sent, what happens when it's found and where calls may go, and reads the answers back as a sentence.
States: watch first, then enforce
| State | What its parts do |
|---|---|
| Draft | Nothing is applied |
| Observing | Guardrail parts log what they find without acting; other parts aren't applied yet |
| Enforcing | Every part is in force |
| Paused | Every part is lifted until someone resumes it, with a reason recorded |
While a policy observes, What enforcing would have done shows the last seven days for the keys it reaches now: findings by category and what would have been done, calls that went outside its region rules' areas, and calls its compliance routes would have sent elsewhere. Start enforcing… shows the same before anything changes.
Which policy acted
Every guardrail finding on a call names the guardrail that decided it and its named policy, and a call a region rule refused names the rule and its policy. On a policy's page, Calls it decided opens exactly those calls in Request logs, and Open in the audit log shows every change made to it.
Who changes them
Organisation admins and Compliance officers Enterprise, and group admins for policies on the teams they run. Organisation viewers read them. What Enterprise includes depends on the features your licence includes; on Community, organisation admins and group admins make and change policies.