Regulations, mapped¶
The problem. A regulation arrives as a long text and a spreadsheet of controls. Turning it into settings, and then showing an auditor that those settings held on every call, is a project of its own. With Vidai, you choose the regulations your organisation follows. For each one, Vidai sets the record retention it asks for, proposes the policies that serve it (watching first, so nothing breaks), shows each control as enforced, observed, partly in place or a gap, and produces the evidence.
What following a regulation does¶
| Community | Enterprise | |
|---|---|---|
| Sets the shortest time each kind of record is kept (and, for minimisation laws, lets you set the longest) | Yes | Yes |
| Offers its recommended policies, made watching first | Yes | Yes |
| Shows each control's coverage, gaps first | — | Enterprise |
| Offers the auditor report and evidence pack for it | — | Enterprise |
What Enterprise includes depends on the features your licence includes. Following a regulation never changes a policy by itself, and never shortens a retention period behind your back.
The regulations and frameworks¶
Mapped control by control¶
For these, Policies › Regulations maps each control to what's in force now, and links the official text.
| Regulation | What Vidai enforces or records | Retention it sets (starting values) |
|---|---|---|
| GDPR (Regulation (EU) 2016/679) | Personal data masked, pseudonymised or blocked before it reaches a model; calls kept in the EU; data processing agreements on record per provider; copies and erasures for data subject requests | No floor; a ceiling: the longest you keep personal data, which you set |
| EU AI Act (Regulation (EU) 2024/1689) | Every AI system with a risk level, an owner and a review date; every call by a high-risk system recorded and always in the auditor's sample; prompt injection stopped; human oversight on record (approvals, overrides, Stop AI traffic); a serious-incident register Enterprise | Call records and tamper-evident records: at least 180 days |
| ISO/IEC 42001 | Roles, AI systems and their owners, suppliers, model access and every change, recorded in one place | Call records and tamper-evident records: at least a year |
| HIPAA Security Rule (45 CFR §164.312) | Health identifiers kept out of models; business associate agreements on record, and a region rule can require one; records of who could call what, and of every call | Call records and tamper-evident records: at least six years |
| PCI DSS v4.0 | Card numbers found with check digits and kept out of models; unused keys suspended automatically; access reviews; provider attestations on record | Call records and tamper-evident records: at least a year; it also expects an archive that can't be altered |
ISO/IEC 42001's mapping has been checked against the official text and says Mapping checked; the others say Beta: which controls a setting covers is our reading, not legal advice, and the official text decides.
Retention and evidence¶
Following these sets the retention they ask for and gives you the downloads Enterprise. Their controls aren't mapped on the Regulations page; the card says No guidance yet, and its retention applies.
| Regulation | What it adds |
|---|---|
| UK GDPR | A ceiling for personal data, as GDPR |
| CCPA (California) | A ceiling for personal data; data subject requests answered call by call |
| India's DPDP Act | A ceiling for personal data; data subject requests answered call by call |
| FCA and MiFID II | Records kept at least five years, including the content of calls by applications that talk with your clients |
| SEC 17a-4 | Records kept at least six years, and the content of calls by applications that talk with your clients at least three; expects an archive that can't be altered |
| ISO/IEC 27001, SOC 2 | Records kept at least a year; also offered as evidence for the framework (below) |
| SOX | Records kept at least seven years; also offered as evidence for the framework (below) |
Gulf laws¶
Built-in packs, each with personal-data guardrails for its country, which find Arabic-Indic digits as well as Latin ones. Region rules keep calls in the region Enterprise, and data subject requests work as for GDPR.
- UAE: UAE PDPL; UAE health data law (Federal Law No. 2 of 2019); DIFC Data Protection Law; DIFC Regulation 10 (AI systems); ADGM Data Protection Regulations 2021; UAE Central Bank (CBUAE) rules
- Saudi Arabia: Saudi PDPL; Saudi NCA Essential Cybersecurity Controls; SAMA Cyber Security Framework
- Qatar: Qatar PDPPL; QFC Data Protection Regulations 2021; Qatar Central Bank AI Guideline
- Bahrain, Oman and Kuwait: Bahrain PDPL; Oman PDPL; Kuwait CITRA Data Privacy Protection Regulation
Each carries a retention preset, so following it sets the retention it asks for.
Where a pack's values are still to be confirmed against the law's implementing rules, its page lists them under what needs a legal check.
Evidence for a framework Enterprise¶
SOC 2, ISO/IEC 27001, ISO/IEC 42001, SOX and NIST AI RMF are frameworks your organisation is audited against. Ask for an evidence pack For: Evidence for SOC 2 (or another) and it carries a file mapping Vidai's records to each of the framework's controls, with the controls that stay your organisation's own. It's evidence for your audit, never a statement that a control is met.
Labels only¶
DORA, Internal and Other tag a policy so you can find it; they set nothing.
Reading coverage Enterprise¶
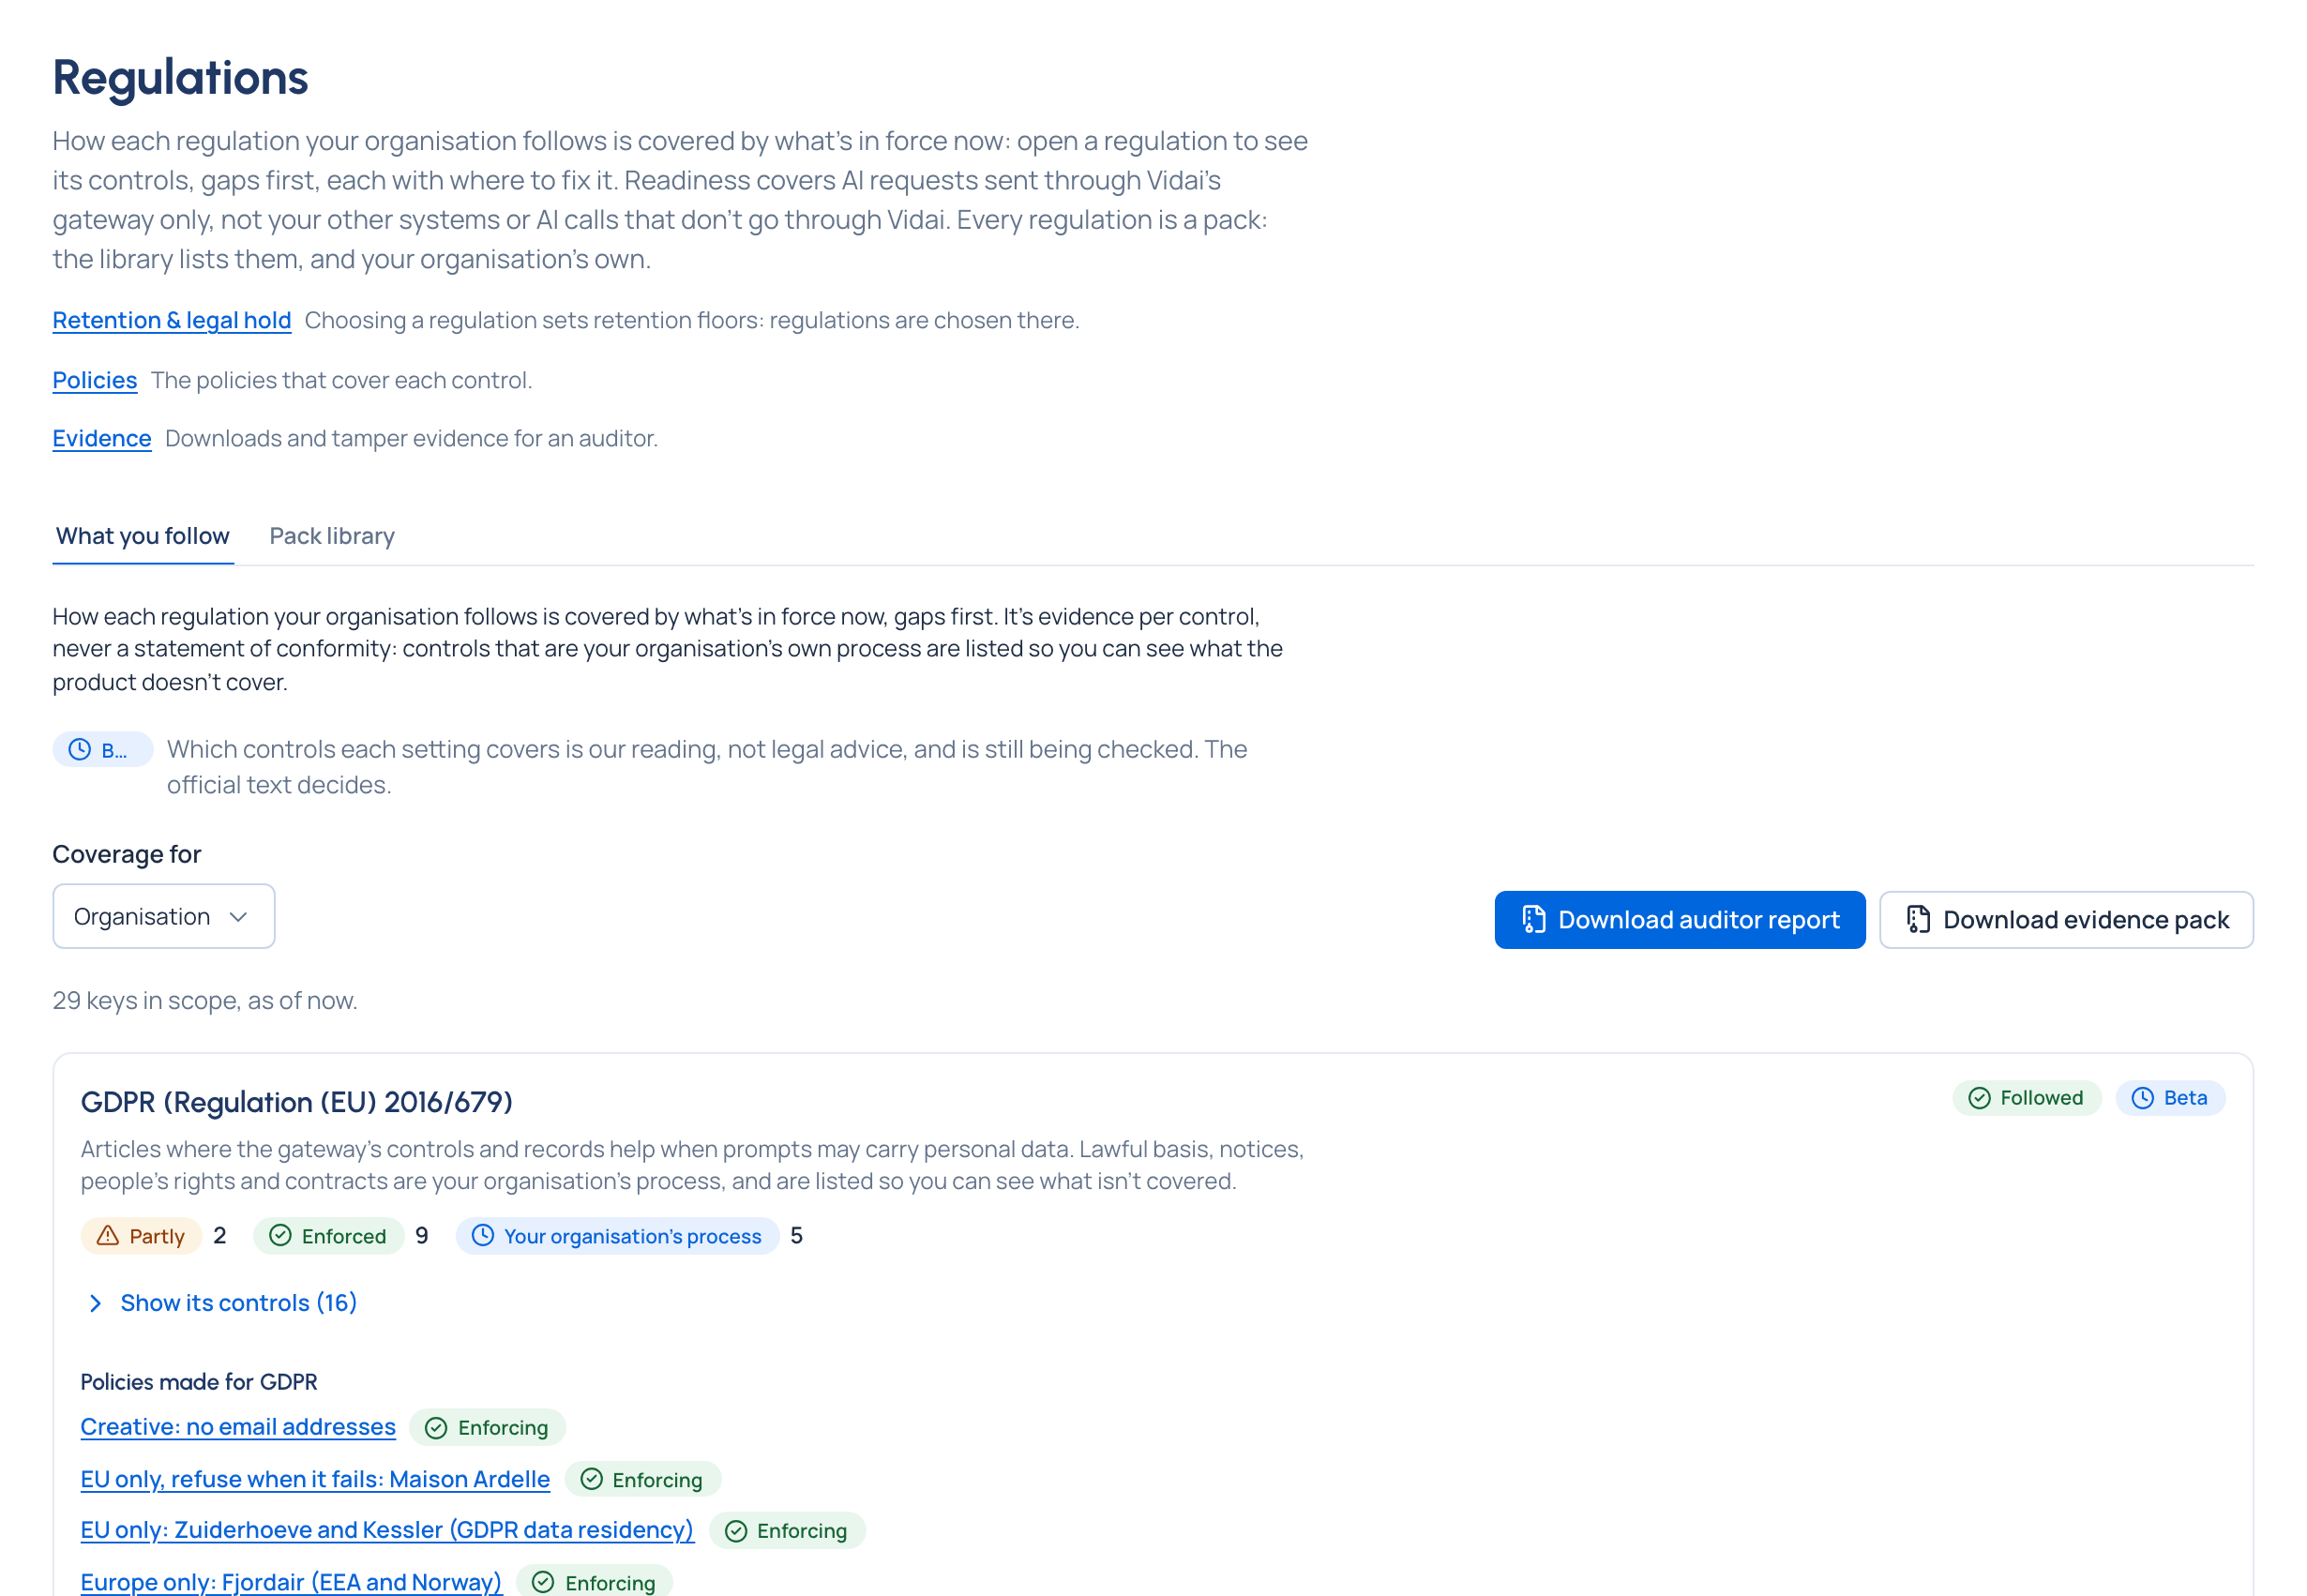
Each followed regulation has a card: Coverage for (the organisation, a team or an application), its controls counted by state, and Show its controls, gaps first.
| State | Meaning |
|---|---|
| Nothing in place | Nothing in scope provides it yet |
| Not checked | It needs VidaiGuard. Where VidaiGuard isn't set up, this is calm: pattern checks still act, and it starts once VidaiGuard is set up. Where it's set up but switched off or not answering, it's a warning |
| Partly | Some keys have it and some don't ("12 keys without it") |
| Observed only | It's watched and logged, but some keys only observe |
| Enforced | Every key in scope has it in force |
| Your organisation's process | The product doesn't cover it; listed so you see what isn't covered. Always last, never hidden |
A control covered by a pack whose VidaiGuard checks don't run right now says Partly by patterns, with why (VidaiGuard isn't set up, its checks are switched off, or it isn't answering), on its row and in its panel. Its pattern checks cover it meanwhile.
Open a control to see What it asks (in our words; the official text decides), How the product helps, each piece of evidence and Where it's set up, the named policies behind it, and, for guardrail evidence, what it did in the last 30 days with up to three calls to open.
Packs: every regulation is versioned¶
Policies › Regulations › Pack library lists every regulation as a pack: what it sets, what it leaves to your organisation, its sources and its history. You can:
- Copy a built-in pack to tighten it for your organisation. A copy may only keep records longer, and each difference asks for a reason, kept with the pack.
- Make a new pack of your own, or import one from another installation. Exported packs carry a checksum and, when your organisation has an evidence key, a signature; an import that was changed after export is refused.
- See when a release brings a new version of a built-in pack. Your copy never changes by itself: its page lists what changed in the original, and Home tells you to review it.
Good to know¶
- Coverage covers AI calls sent through Vidai's gateway, not your other systems, and shows the position now; what was in force on a past day is in the audit log and the evidence pack.
- A policy merely tagged with a regulation never makes it followed or covered. A regulation is followed only when someone chooses it.
- Periods are summaries, not legal advice: your compliance team confirms each one.